
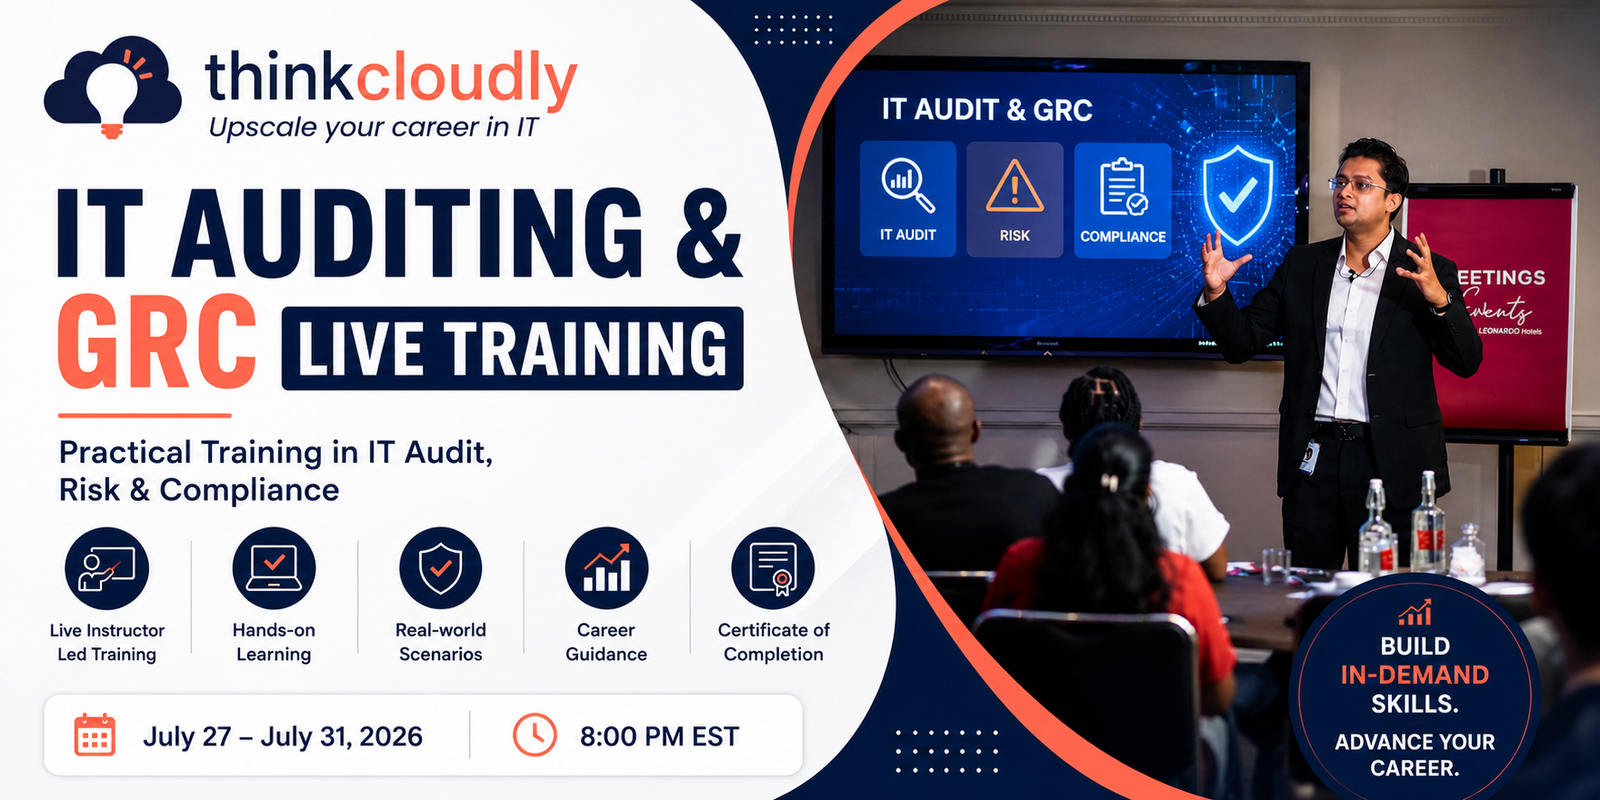

Join this live, practical 5-day online training to build a strong foundation in IT Auditing and Governance, Risk & Compliance (GRC). This beginner-friendly program is designed for aspiring IT auditors, compliance professionals, cybersecurity learners, and career switchers who want practical knowledge they can use for interviews, job roles, and professional growth.
You will learn how IT audits work, how to identify and evaluate risks, how security controls are tested, and how governance and compliance support business and technology operations. The program is structured to help you gain practical knowledge you can use for interviews, job roles, and professional growth.
What You Will Learn
- IT audit lifecycle and core concepts.
- Governance, risk, and compliance fundamentals.
- Risk identification and control assessment.
- Security controls and how they are evaluated.
- Audit processes, reporting, and documentation.
Who This Is For
- Aspiring IT auditors.
- GRC and compliance learners.
- Cybersecurity professionals.
- Internal audit staff.
- Students and career switchers entering IT governance and risk roles.
Why Attend
- Gain practical knowledge in a live instructor-led format.
- Build a strong foundation for IT audit and GRC careers.
- Learn concepts that are useful for interviews, job roles, and professional growth.
- Understand how IT auditing connects with cybersecurity, compliance, and enterprise risk management.
- Receive a certificate of participation.
Event Highlights
- Live online training.
- Structured 5-day learning format.
- Beginner-friendly and career-focused.
- Suitable for learners from technical and non-technical backgrounds.
- Certificate included.
- Limited-time early bird offer.
Agenda
Day 1: Introduction to GRC
- What is Governance, Risk & Compliance.
- GRC domains and core functions.
- Why GRC matters in IT audit and cybersecurity.
- Common GRC career opportunities.
- Job roles and responsibilities.
Day 2: Security Fundamentals
- CIA Triad.
- Types of security controls.
- Administrative controls.
- Technical controls.
- Physical controls.
- How controls support risk reduction and compliance.
Day 3: Personnel Security Controls
- Personnel security concepts.
- Background verification.
- User access management.
- Joiner, mover, and leaver process.
- Practical GRC checks.
Day 4: Vulnerability and Penetration Testing
- Penetration testing overview.
- Vulnerability assessment vs penetration testing.
- Security testing controls.
- Risk identification and reporting.
- How test results support audit and compliance review.
Day 5: Report Review & Audit Checks
- Penetration test report review.
- Finding classification and severity.
- Practical GRC validation checks.
- Audit documentation and evidence review.
- Reporting and closing observations.
About Thinkcloudly
Thinkcloudly is a global EdTech company helping learners transition into IT careers through job-focused training in Cloud, Cybersecurity, Data Science, and GRC. With 140+ industry mentors and 300+ hiring partners worldwide, we’ve trained 10,000+ students and were recognized as the Best Emerging EdTech Company of the Year at Oxford Town Hall, London.